Help Center › Family & Parents
Family portal privacy and security
A feature that shows children's data to adults has exactly one acceptable failure mode: refusing.
The family portal's security model is deliberately boring:
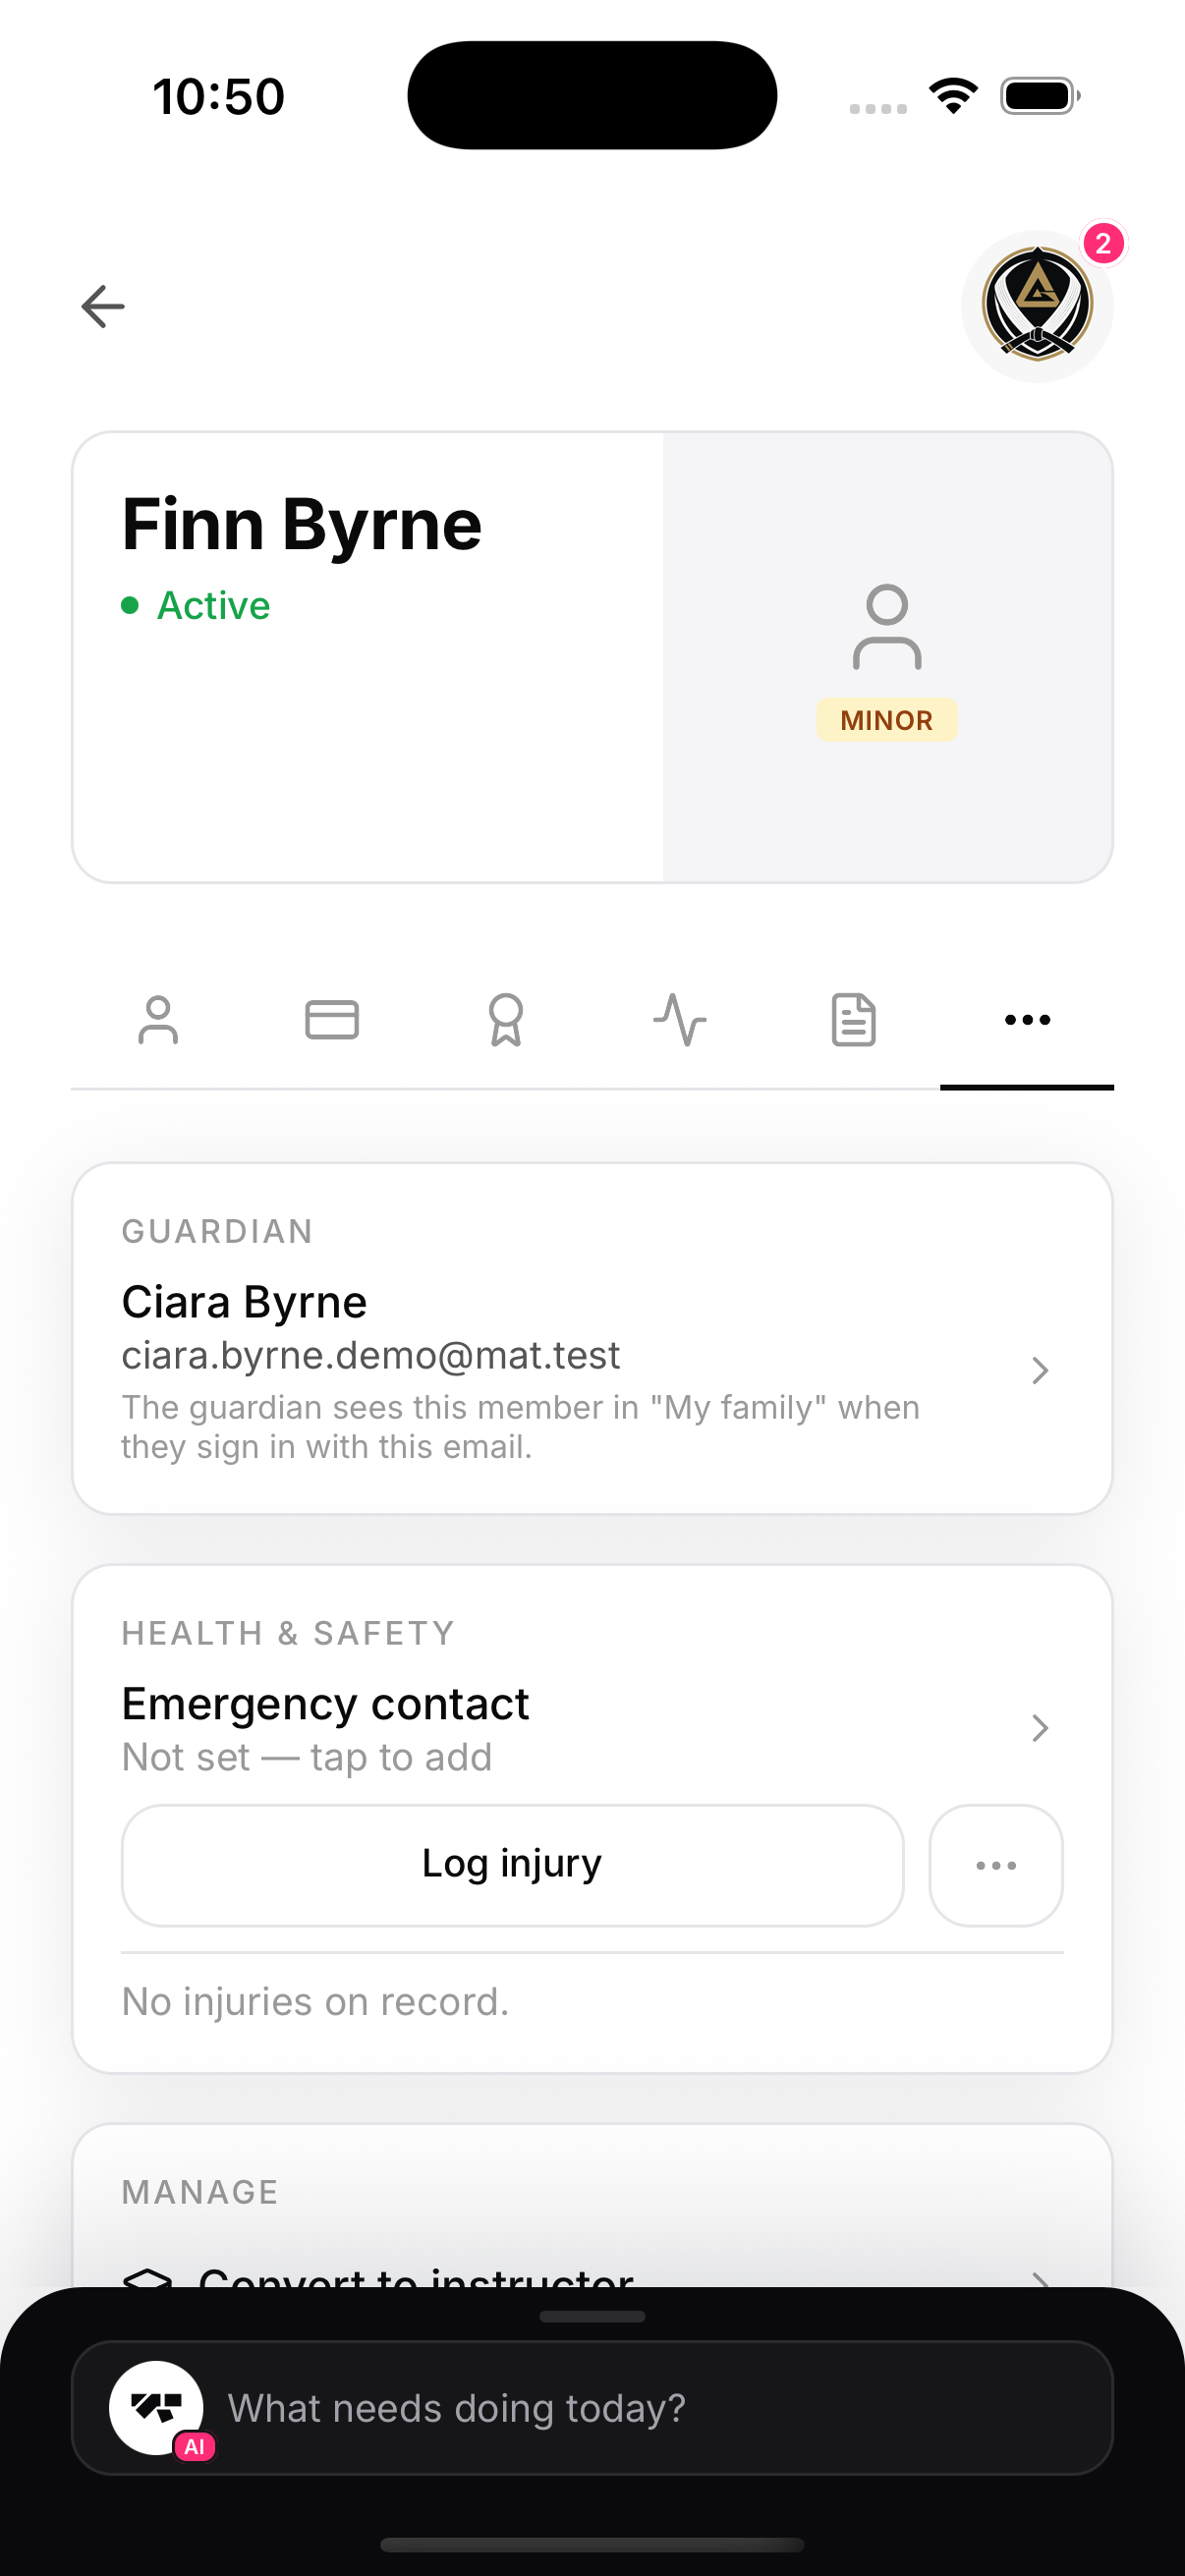
- Authority is the guardian email on the live member record. Every single request re-checks that the caller's verified sign-in email matches the child's current guardian email. Cached links are never trusted on their own; stale ones self-delete.
- Change the email, cut the access. Re-homing a child on the Guardian card instantly moves portal access — there is no lingering session that keeps seeing the old data.
- Scope is per child, per academy. A guardian at academy A sees nothing about academy B unless the same guardian email is on file there too. Uncles, siblings and family friends see nothing, full stop.
- No billing internals, no other members. The child view whitelists exactly the fields a parent needs; payment identifiers and internal keys never leave the server.
- Everything is audited. Guardian bookings are recorded as “booked by guardian”, guardian signatures carry the signer's name, device and timestamp, and it all lands in your academy's audit log.
What parents can't do
Change the child's profile, see class rosters, message other members, or access anything the child themselves couldn't. Profile changes stay with your staff.